5.5 Cloud Armor
WAF and DDoS protection sitting in front of your load balancer.
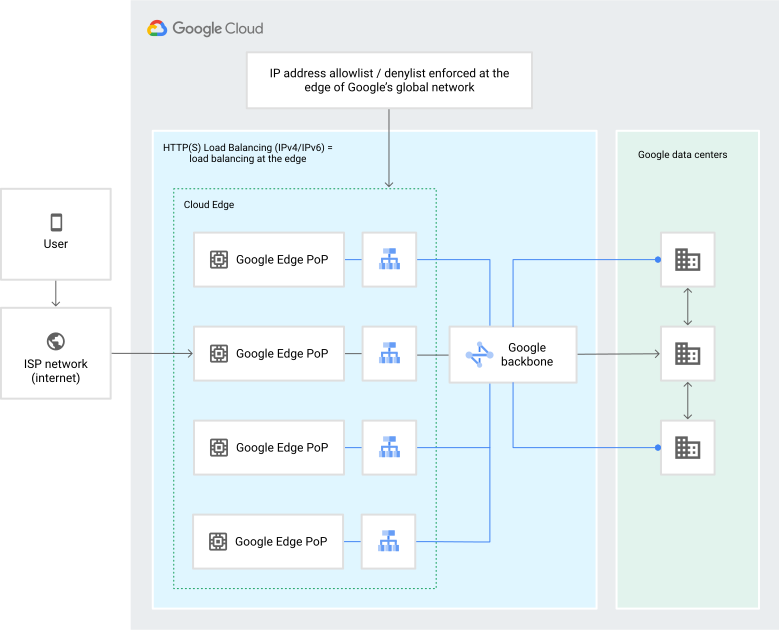
L3/L4 DDoS protection is automatic, free, and requires no configuration; L7 protection (against things like HTTP floods) needs a security policy configured separately — you can apply the OWASP Core Rule Set as a default WAF ruleset (with sensitivity levels 0–4; higher sensitivity catches more but also false-positives more against legitimate traffic), and configure rate limiting. The paid Enterprise tier adds Adaptive Protection (ML-based attack-pattern detection), threat intelligence feeds, and hierarchical security policies — letting you set a baseline at the Org/Folder level that individual projects then layer their own rules on top of.